DPDP Act Compliance Services
Achieve full compliance with India's Digital Personal Data Protection Act, 2023 — from data mapping and consent management to breach response and staff training. Built for startups, enterprises, and government bodies.
What we deliver
- Data mapping Know what personal data you hold and where it flows
- Consent management Capture, record and honor consent, including withdrawal
- DSAR workflows Handle access, correction and erasure requests on time
- Security safeguards Encryption, access controls and tested defenses
- Breach response A rehearsed plan and notification workflow
- Virtual DPO Ongoing guidance and accountability without a full-time hire
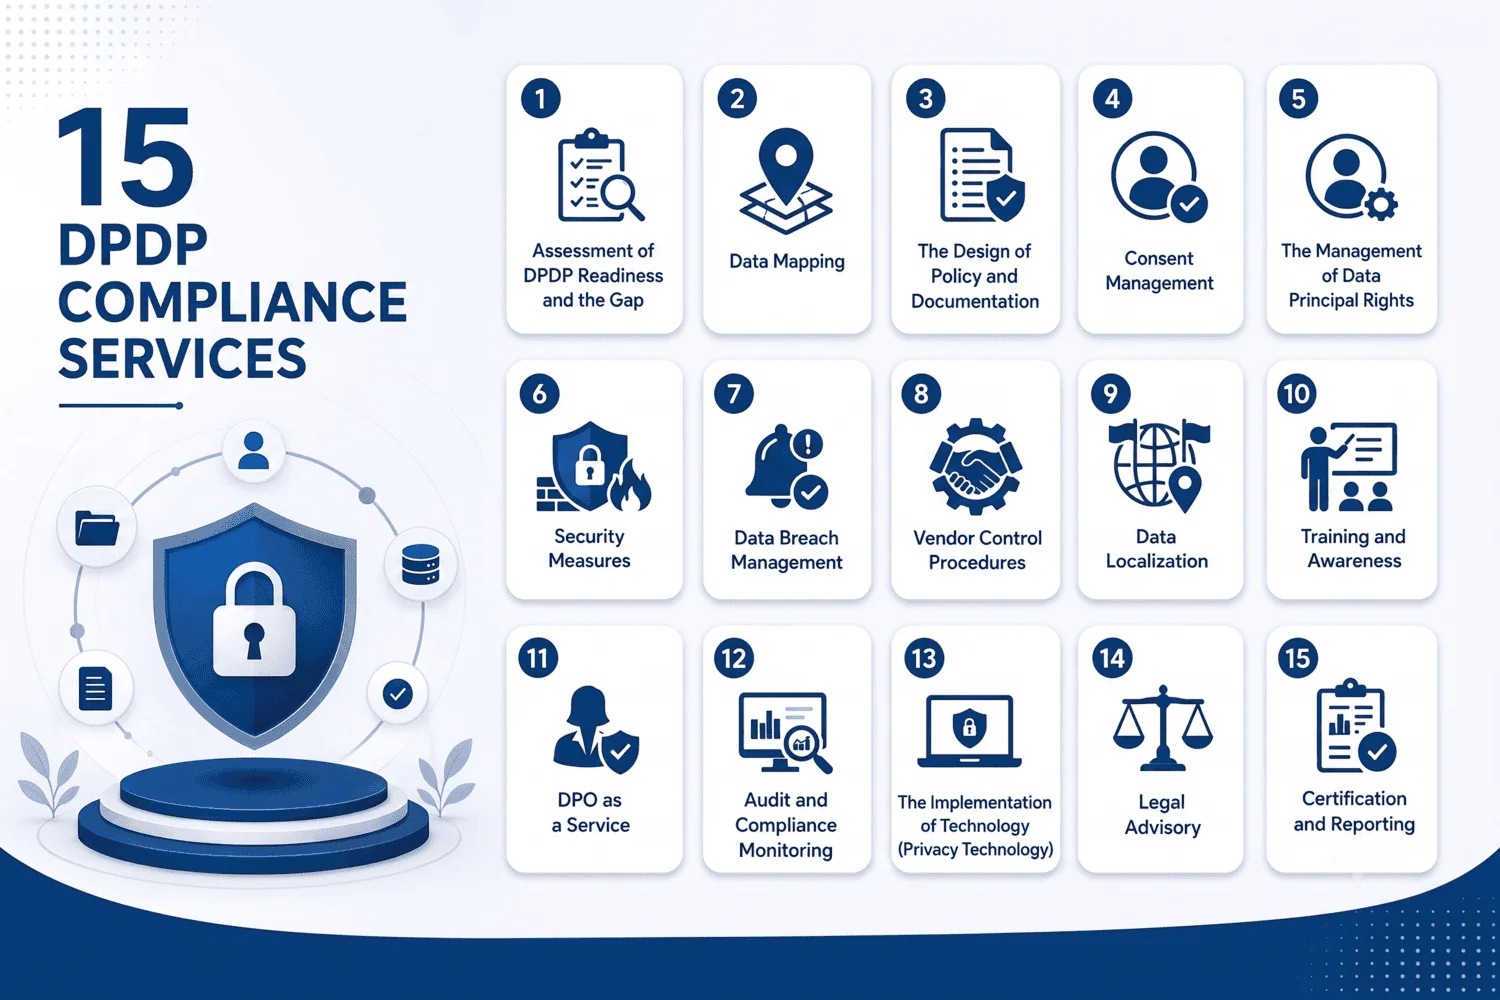
- 15 DPDP compliance services
- 17+ Years of engineering experience
- ISO 27001 Certified information security
- ISO 9001 Certified quality management
- 15+ Industries covered
Which Best Describes Your Organization?
There is no minimum company size for the DPDP Act. Pick the one closest to you and see where we would start.
Startup or MSME
Handling your first customer database and need compliance that fits a small team.
Large Enterprise
Managing personal data across dozens of applications, teams and vendors.
Healthcare, Banking or Insurance
Processing sensitive personal data where privacy and security expectations are highest.
E-commerce, Education or SaaS
Collecting user data through websites and apps that need consent and rights workflows.
Government Body or NGO
Processing personal data digitally and needing clear accountability and grievance handling.
Organization Outside India
Offering goods or services to individuals in India, where the Act can apply to you.
Not sure where your personal data stands?
Our experts will map your data and flag your biggest compliance gaps.
The Nine Pillars of the DPDP Act
A framework spanning individual rights, organisational duty, global trust, and enforcement
-
Individual Rights
Pillar 1: Consent and Notice
Sections 4–6
-
Individual Rights
Pillar 2: Purpose Limitation and Legitimate Uses
Section 7
-
Individual Rights
Pillar 3: Rights of Data Principals
Sections 11–14
-
Organisational Duty
Pillar 4: Data Fiduciary Obligations
Section 8
-
Organisational Duty
Pillar 5: Significant Data Fiduciaries
Section 10
-
Organisational Duty
Pillar 6: Protection of Children's Data
Section 9
-
Global Trust
Pillar 7: Cross-Border Data Transfer
Section 16
-
Enforcement
Pillar 8: Breach Notification and Security
Section 8(6)
-
Enforcement
Pillar 9: Data Protection Board and Enforcement
Sections 18–33
Our DPDP Compliance Services
End-to-end support across the full compliance lifecycle, from initial assessment to ongoing governance
Explore our complete range of DPDP Act Compliance Solutions, built for your industry and scale.
Built for Real Business Problems
Real engagements, real outcomes. Every result below comes from a documented client case study.
Building a CA Services Marketplace for MyTaxProf
MyTaxProf set out to connect clients with Chartered Accountant (CA) firms through one digital platform. D2i Technology built a custom, multi-role CA services marketplace covering service discovery, firm onboarding and verification, and structured service requests.
Read Full Case Study of Building a CA Services Marketplace for MyTaxProfWebsite Redesign at New Life Agency
New Life Agency needed a modern, professional website that truly reflected their reputation. D2i Technology redesigned their digital presence from the ground up — delivering a faster, more intuitive, and fully responsive experience built to support their continued growth.
Read Full Case Study of Website Redesign at New Life AgencyDevOps Transformation at ZiffyCar
ZiffyCar's peer-to-peer car rental marketplace was expanding fast — 50+ cities, thousands of hosts, and booking traffic that spiked hard every weekend. D2i Technology built the DevOps foundation to match that growth, turning a fragmented, contractor-heavy delivery model into a streamlined pipeline that achieved 10× faster releases and a 40% reduction in DevOps spend.
Read Full Case Study of DevOps Transformation at ZiffyCarWhy DPDP Compliance Matters
The DPDP Act, 2023 is India's primary law on how organizations collect, process, store and protect digital personal data. Non-compliance carries real financial risk, with penalties that can reach up to ₹250 crore under the Act's Schedule.
Avoid heavy penalties
Penalties can reach ₹250 crore, weighed by the nature, gravity and duration of the breach.
Build customer trust
Clear consent and respected rights show people you take their data seriously.
Respect individual rights
Access, correction, erasure and grievance redressal handled on time.
Reduce breach impact
Security safeguards and a rehearsed response plan limit the damage.
Stay audit-ready
Documented practices and reports make audits and partner reviews straightforward.
Where Should You Start?
Every organization begins somewhere different. Here is how we would think about it.
| If you need... | Consider... |
|---|---|
| To know how far you are from compliance | Readiness and gap assessment |
| To find out what personal data you hold | Data mapping |
| Valid consent and easy withdrawal in your app | Consent management implementation |
| A way to answer access and erasure requests | DSAR and grievance workflows |
| A DPO without a full-time hire | DPO as a Service |
| To be ready if a breach happens | Breach response plan and simulations |
Our DPDP Compliance Process
A structured 6-stage process that takes you from unmapped data to full DPDP compliance
-
Step 01
Discover
Data mapping across systems, vendors and third parties.
-
Step 02
Assess Gaps
Compare current practices against DPDP requirements.
-
Step 03
Design Policy
Privacy notices, consent flows and internal policies.
-
Step 04
Implement
Consent, DSAR and grievance workflows built into your systems.
-
Step 05
Harden
Encryption, access controls and breach response plans.
-
Step 06
Train and Monitor
Employee training and ongoing compliance reviews.
What Happens After You Contact D2i?
No big commitment up front. Here is what the first few weeks look like.
-
Step 1: 30-minute discovery call
We listen to how you handle personal data today.
-
Step 2: Readiness assessment
We review your data practices against the Act.
-
Step 3: Solution proposal
Scope, team and estimate in writing.
-
Step 4: Compliance roadmap
Priorities, milestones and who does what.
-
Step 5: Start implementing
Your team is onboarded and the first workstream begins.
We Don't Stop at Policy Documents
Compliance is built directly into your websites, apps and internal tools, so it keeps working after the paperwork is signed.
Engineering-Led
Consent, DSAR and security workflows implemented directly in code, not just described in a PDF.
Consent-Ready
Consent that is captured, recorded, honored and easy to withdraw.
On Time
Requests and grievances tracked against their timelines.
Secure
Safeguards tested rather than assumed, backed by ISO 27001 certified processes.
Continuously Monitored
Regular reviews keep you compliant as regulations and your business evolve.
Audit-Ready
Reports and records that show your compliance position clearly.
Privacy and Security Built Into Your Systems
Compliance shouldn't depend on people remembering a policy. We build it into the way your systems collect, use and protect personal data.
-
Map
A live inventory of personal data, where it sits and who touches it.
-
Consent
Valid consent captured, stored and honored, including withdrawal.
-
Rights
Access, correction and erasure requests routed and tracked.
-
Protect
Encryption, masking and access controls, tested regularly.
-
Respond
A rehearsed breach plan with notification workflows.
- DPDP Act 2023
- ISO 27001
- Valid consent
- Data minimization
- Purpose limitation
- Encryption and masking
- Access controls
- Breach simulations
Regulations & Standards We Align With
We build DPDP programs that also hold up against related regulations and security frameworks your business may need
Core Regulation
- DPDP Act 2023
- IT Act 2000
- MeitY Rules
Global Privacy
- GDPR
- CCPA
- ISO 27701
Security Standards
- ISO 27001
- SOC 2
- NIST CSF
Sector Specific
- RBI Guidelines
- IRDAI
- SEBI
Not Sure Where to Start?
Tell us where you are and what you need. We will suggest a starting point.
You're probably looking for
Choose a stage to see our suggestion
Your answers stay on this page. Nothing is sent until you contact us.
Engagement Models for DPDP Compliance
The digital personal data protection act sets clear expectations for how businesses handle personal data. Whether you need a one-time audit or ongoing governance, we offer flexible engagement models matched to your organization's size and risk profile.
One-Time Assessment
A structured audit of your current data practices against DPDP requirements, delivered as a clear gap report and remediation roadmap.
- Data mapping and gap analysis
- Prioritized remediation roadmap
- Fixed timeline and deliverable
Best for: Organizations starting out or preparing for an audit.
Ongoing Compliance Retainer
Continuous governance with a Virtual DPO, periodic reviews, and updates as regulations, guidance and your business evolve.
- Virtual DPO and advisory access
- Quarterly compliance reviews
- Predictable monthly billing
Best for: Organizations that need steady oversight without a full-time hire.
Fixed-Scope Implementation
Hands-on build-out of consent flows, DSAR workflows and security safeguards into your existing websites, apps and systems.
- Clear scope and milestones
- Engineering-led delivery
- On-time go-live
Best for: Teams with a roadmap that now need it built.
Why Companies Work With D2i
Our teams don't just hand you a policy document, they build compliance directly into your product.
Engineering-Led Compliance
Our developers implement consent, DSAR and security workflows directly in code.
Privacy, Security and Engineering Together
Policy work and hands-on engineering from one team.
ISO 27001 Certified Security
Safeguards we implement meet recognized international standards.
ISO 9001 Certified Quality
Consistent quality and reliable delivery across every compliance engagement.
Ongoing Monitoring
We don't disappear after go-live. Reviews keep you compliant as regulations evolve.
Cost-Effective Engagement
India-based delivery scoped to fit startups, MSMEs and large enterprises alike.
What Clients Say
In recognition of exceptional performance, dedication, hard work, passion, and commitment to excellence — D2i Technology’s invaluable contribution continues to make a significant impact in support of our All Hazards, One Health, One Nature mission.
Allison A. Sakara
Co-Founder & Executive Director, High Alert Institute
Their DevOps Services in USA helped us significantly reduce deployment time and infrastructure costs. D2i Technology streamlined our CI/CD pipelines and improved system stability. The results were visible within weeks, and their DevOps expertise truly made a difference.
DevOps Services & Solutions (USA)
D2i Technology is a highly dependable Web Development Company in India. From requirement gathering to final delivery, their team demonstrated strong technical expertise and ownership. The final product was robust, user-friendly, and built exactly as envisioned.
Web Development Company (India)
Frequently Asked Questions
The questions we hear most before a project starts.
Get Ahead of DPDP Compliance with D2i Technology
Whether you need a one-time compliance assessment or an ongoing Virtual DPO partner, D2i Technology is ready. Let's protect your customers' data and your business today.
No obligation. Start with a 30-minute discovery conversation.