- Data Privacy & Compliance
- October 19, 2026
We Thought Our Business Was Ready for the DPDP Act… Until One Customer Asked a Simple Question
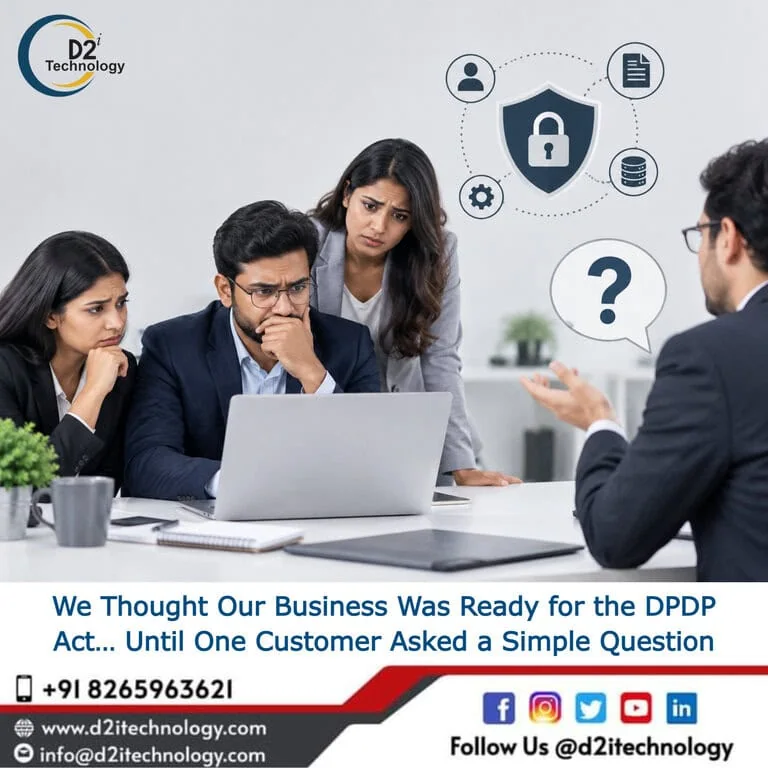
“We’ve secured our applications, implemented SSL, and our customer data is safe. We’re already compliant.”
That was the confident response Rakesh, the Founder and CEO of a growing SaaS company in India, gave during a quarterly leadership meeting.
Over the past five years, his team had built multiple enterprise applications for clients in healthcare, finance, education, and eCommerce. Their developers followed secure coding practices, penetration tests were conducted regularly, and cloud infrastructure was monitored around the clock.
Business was growing rapidly.
Then one of their largest enterprise customers sent an email.
“Before we proceed with the contract renewal, could you please share your DPDP compliance documentation, Data Protection Assessment, Consent Management process, and Privacy Governance Framework?”
Rakesh smiled at first.
“That should be easy,” he thought.
But after speaking with his engineering manager, legal advisor, DevOps lead, and project managers, he realized something unexpected.
No one had a complete answer.
The Assumption That Many Businesses Make
Like many organizations, Rakesh believed cybersecurity and privacy were the same thing.
His company had:
- Firewalls
- Encrypted databases
- Multi-factor authentication
- Secure cloud infrastructure
- Regular backups
- Vulnerability assessments
- Penetration testing
Surely that meant they were compliant.
Not exactly.
Security protects systems.
DPDP Compliance protects people’s personal data and defines how organizations collect, process, store, share, and delete that data responsibly.
That realization completely changed the way his company approached compliance.
Understanding the DPDP Act
The Digital Personal Data Protection (DPDP) Act, 2023 is India’s landmark privacy legislation that establishes how organizations should process digital personal data while protecting the rights of individuals.
Whether you’re a startup, SaaS company, healthcare provider, financial institution, educational platform, or enterprise software company, if you collect personal information, the DPDP Act likely applies to your business.
The law isn’t only about avoiding penalties.
It’s about building trust.
A Simple Question Changed Everything
The legal advisor asked Rakesh one question:
“Can you tell me exactly where all your customers’ personal data is stored?”
The room went silent.
Everyone had a different answer.
Some data was stored in the CRM.
Some lived in cloud storage.
Employee records were in HR software.
Marketing teams had spreadsheets containing customer information.
Support teams stored attachments inside ticketing systems.
Developers had database backups on internal servers.
Nobody had a complete picture.
That was the beginning of their DPDP Readiness Assessment.
The Hidden Challenge of Data Discovery
Over the next two weeks, the team conducted a Data Discovery and Data Mapping exercise.
They discovered personal information across:
- CRM systems
- Email platforms
- Marketing tools
- HRMS
- ERP applications
- Customer support software
- Mobile applications
- Shared folders
- Cloud storage
- Backup servers
- Third-party SaaS platforms
The company wasn’t collecting too much data intentionally.
It had simply accumulated over the years.
Without realizing it, they had created unnecessary privacy risks.
Consent Management Was More Complicated Than Expected
Rakesh assumed every customer had already agreed to the company’s Privacy Policy.
The compliance consultant asked another question.
“Can you prove when each customer gave consent, what they agreed to, and whether they can withdraw it?”
Again, there was silence.
Some applications captured consent.
Others didn’t.
Different products displayed different privacy notices.
Marketing forms collected data without recording consent history.
The team quickly realized that Consent Management was not just a checkbox—it required consistent processes, audit trails, and transparency across every application.
Privacy Is More Than a Privacy Policy
Many organizations believe updating their website’s Privacy Policy is enough to achieve DPDP Compliance.
Rakesh learned otherwise.
Privacy must be built into business processes.
The company created:
- A Data Governance Framework
- Data Retention Policies
- Data Classification Standards
- Vendor Assessment Procedures
- Incident Response Plans
- Employee Privacy Training
- Secure Data Handling Guidelines
Compliance became part of the organization’s culture—not just its documentation.
Third-Party Vendors Became a Priority
Like most businesses, Rakesh’s company relied on several external services.
These included:
- Payment gateways
- Email service providers
- SMS gateways
- Cloud hosting
- Analytics platforms
- Customer support tools
- Marketing automation software
Each integration processed customer information.
Each represented a potential compliance risk.
The company introduced Vendor Privacy Assessments and reviewed agreements with every technology partner to ensure they followed appropriate data protection practices.
Employee Awareness Made the Biggest Difference
One surprising discovery had nothing to do with technology.
It involved people.
Developers occasionally downloaded production databases for debugging.
Support teams shared screenshots containing customer information.
Employees stored files on personal devices while working remotely.
None of these actions were intentional.
But each increased privacy risk.
Rakesh introduced regular employee awareness sessions covering:
- Secure data handling
- Password security
- Phishing awareness
- Safe file sharing
- Privacy obligations
- Remote work security
- Data retention
- Incident reporting
Within a few months, the company noticed fewer security incidents and better compliance across teams.
Compliance Improved Product Quality
Initially, developers worried that DPDP Compliance would slow them down.
Instead, something unexpected happened.
Engineering teams began asking better questions before building new features.
- Do we really need this information?
- Can we collect less data?
- How long should we retain it?
- Can customers delete their information?
- Is this API secure?
- Are we encrypting sensitive fields?
By embedding Privacy by Design into the development lifecycle, applications became simpler, more secure, and easier to maintain.
Customers Started Asking Different Questions
A year earlier, prospective customers had asked about pricing and features.
Now they also wanted to know:
- Do you conduct a DPDP Compliance Audit?
- Can you share your DPDP Readiness Assessment?
- How do you manage consent?
- What is your Data Governance Framework?
- How do you protect customer information?
- Do you perform Privacy Risk Assessments?
- How do you respond to data breaches?
Instead of scrambling for answers, Rakesh’s team had documentation ready.
That confidence helped close enterprise deals faster.
Common Mistakes Organizations Make
During his compliance journey, Rakesh noticed several recurring mistakes:
- Assuming cybersecurity alone ensures compliance.
- Collecting more personal information than necessary.
- Ignoring third-party vendors.
- Storing customer data indefinitely.
- Not documenting consent.
- Failing to classify personal data.
- Neglecting employee awareness.
- Treating compliance as a one-time project.
These issues are common—but they can be addressed with the right strategy and governance.
Building a DPDP Compliance Roadmap
Rakesh’s organization adopted a structured implementation approach:
Phase 1: DPDP Readiness Assessment
- Data Discovery
- Data Mapping
- Gap Assessment
Phase 2: Governance
- Privacy Policies
- Data Governance Framework
- Data Classification
- Consent Management
Phase 3: Technology
- Encryption
- Secure Application Development
- Access Controls
- Monitoring
- Backup & Recovery
Phase 4: Validation
- DPDP Compliance Audit
- Security Testing
- Vulnerability Assessment
- Privacy Review
Phase 5: Continuous Improvement
- Employee Training
- Vendor Reviews
- Annual Compliance Assessments
- Policy Updates
This roadmap transformed compliance from a reactive task into an ongoing business capability.
How D2i Technology Helps Organizations Achieve DPDP Compliance
At D2i Technology, we help organizations move beyond checklists and build practical, scalable privacy programs that align with the Digital Personal Data Protection (DPDP) Act, 2023.
Our services include:
- DPDP Readiness Assessment
- DPDP Compliance Consulting
- DPDP Gap Assessment
- DPDP Compliance Audit
- Data Discovery & Data Mapping
- Consent Management Implementation
- Privacy Policy Review
- Data Governance Framework Development
- Privacy Risk Assessment
- Vendor Privacy Assessment
- Secure Software Development
- Cloud Security & DevOps
- Cybersecurity Testing
- AI-Powered Compliance Solutions
- Digital Accessibility & Quality Engineering
Whether you’re a startup preparing for your first enterprise customer or a large organization modernizing your privacy practices, our team helps you implement compliance without slowing innovation.
Rakesh’s Biggest Lesson
Looking back, Rakesh realized the DPDP Act wasn’t just another regulation.
It was an opportunity.
An opportunity to better understand his organization’s data.
To improve security.
To strengthen governance.
To build customer trust.
And ultimately, to create better software.
Today, when potential clients ask about DPDP Compliance, Data Protection Assessments, Consent Management, or Privacy Governance, his team no longer sees those questions as obstacles.
They see them as proof that trust has become one of the most valuable assets a business can earn.
Because in today’s digital economy, customers don’t simply buy software.
They buy confidence that their personal data is protected.
And organizations that invest early in DPDP Compliance, Data Privacy Compliance, Privacy by Design, and Data Governance will be the ones that earn that confidence for years to come.
Frequently Asked Questions
Don't Wait for a Customer Email to Start Your DPDP Compliance Journey
D2i Technology helps organizations across India build practical DPDP compliance programs - from readiness assessments and data mapping through consent management, security testing, and ongoing governance. Whether you're preparing for an enterprise contract or modernizing your privacy practices, we'll help you get there without disrupting your business.